> For the complete documentation index, see [llms.txt](https://support.powerio.com/hub/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://support.powerio.com/hub/orbit/en/users-and-roles/rollen-und-berechtigungen.md).
# Roles and permissions
Roles determine what users in powerIO Orbit may see and change. The page compares the permissions of all roles at a glance.
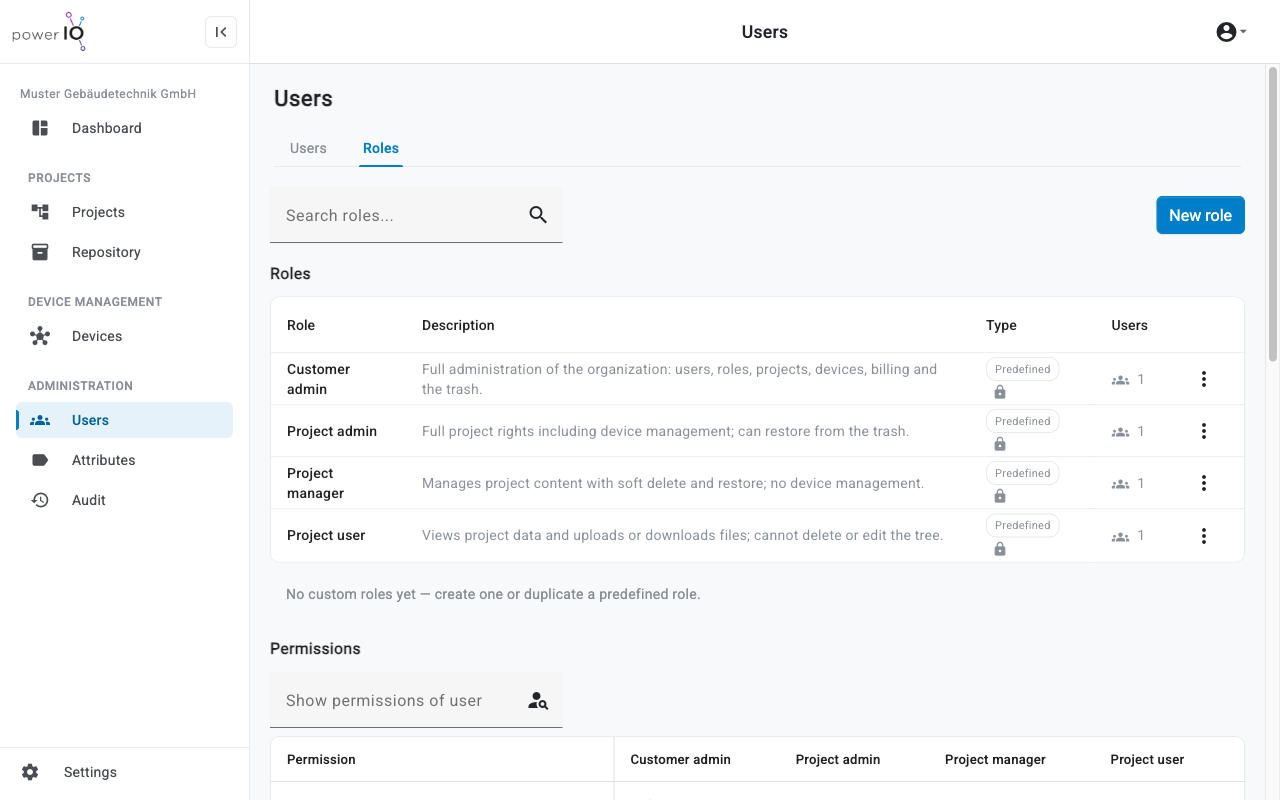
Every organization starts with four predefined roles, from **Customer admin** to **Project user**. For special tasks, a **Customer admin** in the tab **Roles** creates custom roles.
Predefined roles in the Roles tab
## Predefined roles
The predefined roles apply to the entire organization and cannot be changed.
| Role | Tasks |
| ------------------- | ------------------------------------------------------------------------------------------------------- |
| **Customer admin** | Manages the entire organization with users, roles, projects, devices, and the trash. |
| **Project admin** | Has all project permissions, including device management, and restores content from the trash. |
| **Project manager** | Edits project content, moves content to the trash, and restores it. This role does not manage devices. |
| **Project user** | Views project data and uploads and downloads files. This role does not edit or delete the project tree. |
If a user has multiple roles, the permissions of all roles are combined.
## Permissions of the predefined roles
The table shows the permissions as they appear in the **Roles** under **Permissions** tab. Whether a function is available also depends on your organization's plan.
| Permission | Customer admin | Project admin | Project manager | Project user |
| -------------------------------------- | :------------: | :-----------: | :-------------: | :----------: |
| **See project data** | ✓ | ✓ | ✓ | ✓ |
| **Upload files** | ✓ | ✓ | ✓ | ✓ |
| **Download files** | ✓ | ✓ | ✓ | ✓ |
| **Create and edit the project tree** | ✓ | ✓ | ✓ | |
| **Delete project data (to the trash)** | ✓ | ✓ | ✓ | |
| **Restore from the trash** | ✓ | ✓ | ✓ | |
| **Run archive analysis** | ✓ | ✓ | ✓ | |
| **Delete software archives** | ✓ | ✓ | | |
| **Manage the attribute catalog** | ✓ | ✓ | | |
| **Manage devices** | ✓ | ✓ | | |
| **Access all device data** | ✓ | ✓ | | |
| **Permanently delete from the trash** | ✓ | | | |
| **List users** | ✓ | | | |
| **Manage users** | ✓ | | | |
| **Manage roles** | ✓ | | | |
| **Manage user groups** | ✓ | | | |
| **Update customer data** | ✓ | | | |
| **Read billing information** | ✓ | | | |
| **Update billing information** | ✓ | | | |
With **Show permissions of user** check which permissions a specific user has from all their roles.
## Create a custom role
A custom role tailors permissions exactly to a task, for example for a service partner.
{% stepper %}
{% step %}
### Open the Roles tab
Click in the sidebar on **Users** and select the tab **Roles**.
{% endstep %}
{% step %}
### Open the New role dialog
Click on **New role**. The dialog **New role** appears.
{% endstep %}
{% step %}
### Define the role
Enter under **Name** the name and under **Description** enter a short description. Under **Permissions** select the role's permissions.
{% endstep %}
{% step %}
### Save role
Click on **Create**. The role appears in the list with the type **Custom**.
{% endstep %}
{% endstepper %}
Alternatively, copy a predefined role via its menu with **Duplicate as custom role** and customize the copy.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation dynamically by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://support.powerio.com/hub/orbit/en/users-and-roles/rollen-und-berechtigungen.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `build a script that syncs our docs to a CMS` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.